Security
Elementor CSRF Flaw Puts WordPress Hosts on Update Alert
Patchstack says Elementor 4.3.0 and 4.3.1 allowed crafted links to bypass REST API CSRF checks, raising the risk of unwanted administrator actions on WordPress sites.
Sharp briefings on web hosting, internet domains, cloud infrastructure and the fragile plumbing of being online.
Patchstack says Elementor 4.3.0 and 4.3.1 allowed crafted links to bypass REST API CSRF checks, raising the risk of unwanted administrator actions on WordPress sites.
WordPress site operators have another core update to prioritize after researchers disclosed technical details and a proof-of-concept for a vulnerability dubbed Click2Shell. BleepingComputer reports that the issue is […]
Amazon Web Services has made its new Amazon EC2 T8i instances generally available, adding a lower-cost burstable option for small web workloads, staging environments, microservices and other low-to-moderate […]
Vercel has expanded its Spend Management controls to Enterprise customers on Flexible Commitment plans, giving larger teams the same budget guardrails already available on Pro plans at no […]
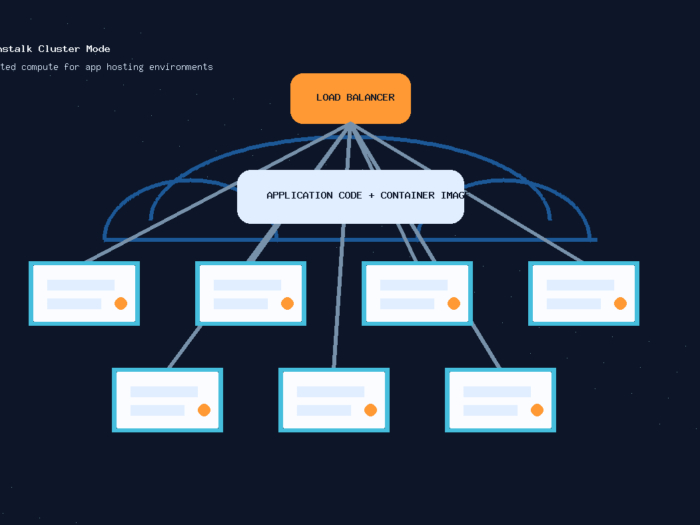
AWS Elastic Beanstalk Cluster Mode gives teams a service-operated compute option for running source-code or container-based web applications.
Hostinger says a LiteSpeed Web Server zero-day was used against one Brazil shared-hosting server, with LSWS 6.3.7 Build 2 deployed across its fleet the same day.
Firebase has added spend caps in public preview for several usage-based services, giving app and site teams a more direct way to limit runaway bills from serverless workloads. […]